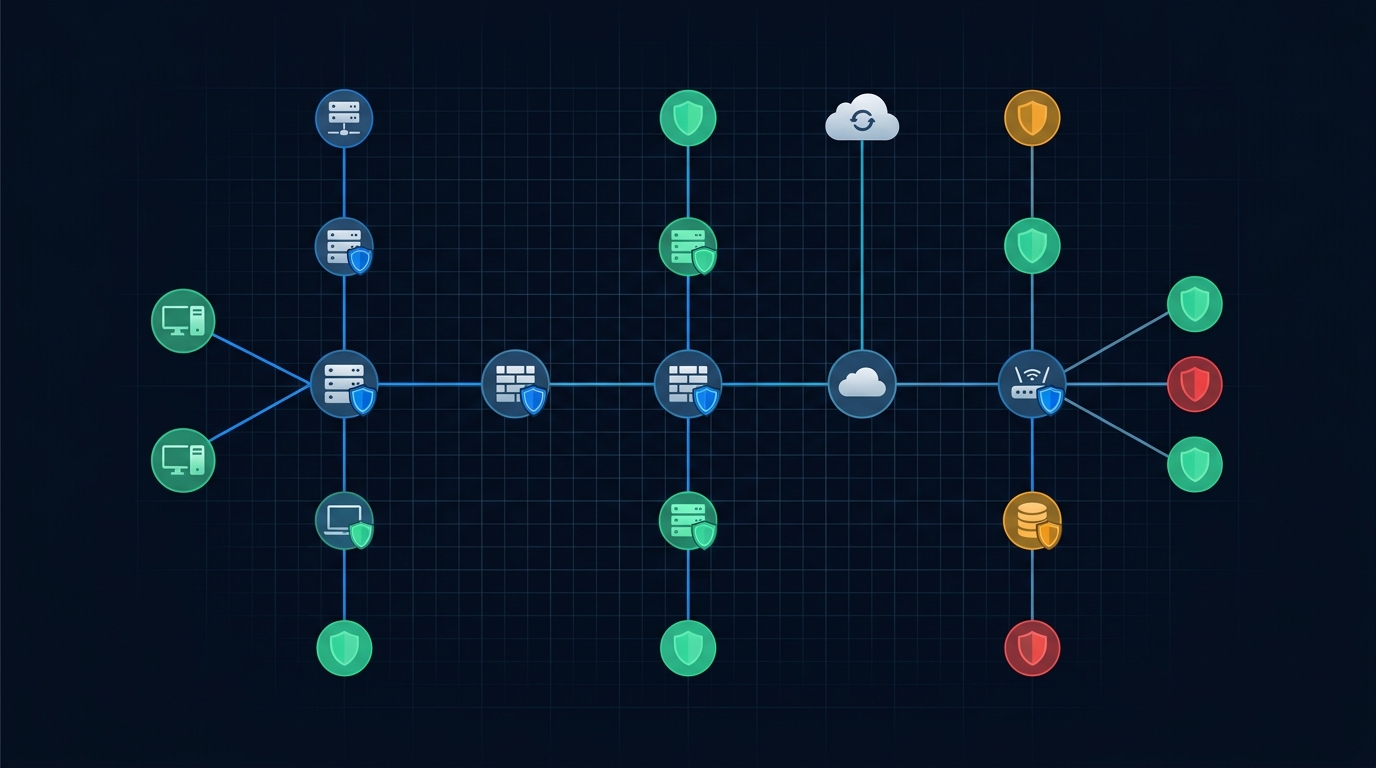
NITECHSPARK helps MSMEs assess their cybersecurity and IT infrastructure, identify critical weaknesses, and implement practical remediation.
Most MSMEs have IT risks they don't know about. These aren't hypothetical — they're common weaknesses found in businesses like yours, every day.
Services and ports unintentionally exposed to the internet — often undetected until an attacker finds them first.
Shared administrator accounts, former employees retaining system access, and missing multi-factor authentication.
Critical security updates missing across Linux and Windows servers, leaving known vulnerabilities open to exploitation.
No visibility into system availability, errors or security events. Issues go unnoticed until they cause business disruption.
Backups exist on paper, but recovery has never been tested. Data thought to be safe may not actually be recoverable.
Expired SSL certificates, misconfigured DNS, weak domain security and exposed external services creating unnecessary risk.
Insecure VPN configurations, direct RDP/SSH exposure, and inadequate controls on remote workers and vendors.
Overly permissive firewall rules, missing network segmentation, and inadequate perimeter security configurations.
No documented process for responding to a breach, ransomware event or service outage — discovering the gap during a crisis.
Unaddressed IT vulnerabilities can result in ransomware and data loss, business interruption and downtime, unauthorized access to customer and financial data, costly recovery operations, and damage to customer trust. Understanding your actual risk posture is the first step to managing it.
We assess your company's IT infrastructure and cybersecurity posture, identify the risks that matter to your business, and help you fix them.
We review your agreed IT environment, identify security and infrastructure weaknesses, classify the risks by impact and priority, and provide a practical remediation roadmap your team can act on.
After the assessment, NITECHSPARK can implement the agreed corrective actions — hardening servers, fixing access controls, improving backups, configuring firewalls, and improving your overall security posture.
NITECHSPARK performs a structured assessment of your authorized IT environment to identify cybersecurity weaknesses, infrastructure risks and operational gaps across nine key areas.
Servers, endpoints, network devices, critical business applications and cloud services — identifying what exists and what matters.
Firewall configuration, VPN setup, remote access controls, exposed services and basic network security posture.
Linux and Windows hardening, patch status, running services, privileged access controls and security configuration.
Operating system updates, endpoint protection status, local administrator privileges and device security hygiene.
User accounts, administrative privileges, shared accounts, MFA implementation and access lifecycle management.
Backup coverage, retention policies, isolation from live systems, recovery verification and business continuity considerations.
SSL/TLS certificate status and configuration, DNS security, domain settings and external web exposure.
System availability monitoring, log collection, alert configuration and security visibility across the environment.
Incident readiness, defined security ownership, vendor and third-party access controls, and basic security procedures.
A professional assessment report with everything you need to understand your risk and take action.
A clear, non-technical overview of the key findings and overall risk posture — written for business owners and decision makers.
An aggregated assessment of your current security and infrastructure status, broken down by assessment area.
Every identified issue classified as Critical, High, Medium or Low — with technical evidence and context for each finding.
Each finding explained in business terms — what could happen if the risk is not addressed, not just technical descriptions.
Specific, actionable corrective actions for each finding — prioritized by risk level and practical implementation difficulty.
A structured remediation plan showing what should be addressed immediately, in the short term, and over the next 90 days.
A separate proposal for NITECHSPARK to implement the agreed corrective actions, scoped and priced based on actual findings.
The assessment report is designed to be understood by business owners and IT staff — not just cybersecurity specialists. Every finding is explained in practical terms with a clear recommended action.
After the assessment, NITECHSPARK can implement the agreed corrective actions to improve the security and reliability of your IT environment. We translate the findings directly into practical implementation work.
Request RemediationCorrective actions are implemented based on assessment findings. Scope and pricing are agreed separately — we do not offer fixed remediation packages.
A straightforward, structured engagement — no surprises, no scope creep.
Whether you run servers on-premise, use cloud platforms, or depend on business applications and websites — NITECHSPARK can assess your authorized environment and identify practical risks.
NITECHSPARK is based in Erode, Tamil Nadu. Our primary focus is helping local MSMEs understand and reduce their IT security risks — with practical, affordable assessments designed for real businesses.
We also serve businesses across India. Remote assessments are available.
Three assessment options for different business sizes. Final pricing is confirmed after a brief discovery conversation based on your actual environment.
Final pricing depends on infrastructure size, number of systems, locations and assessment scope.
All assessments are conducted within a written, agreed scope. Remediation is quoted separately based on findings and implementation requirements.
The assessment does not guarantee complete security. It identifies risks within the agreed scope at the time of assessment.
NITECHSPARK uses purpose-built security tools as part of our technical assessment capability.
NiteSentinels (SecureScope) is NITECHSPARK's Linux security assessment and hardening technology — used to identify configuration weaknesses, security gaps and hardening opportunities in Linux server environments.
CyberScan is a web and network security scanning utility used to support NITECHSPARK's assessment work — providing port scanning, SSL analysis, DNS lookup and external exposure analysis.
The following are illustrative assessment scenarios based on common MSME environments. They represent the types of findings a structured assessment typically uncovers.
A manufacturing business running production data on a Linux server had not undergone a structured security review in over two years.
A textile export company with 45 employees, two servers and a business website requested a full infrastructure assessment before a compliance audit.
Following a professional assessment, a trading company engaged NITECHSPARK to implement agreed corrective actions across their server and access environment.
These are illustrative scenarios. They represent typical MSME assessment findings. No real client data or names are used.
NITECHSPARK is a registered MSME — like the businesses we serve. We operate with the same constraints, and we understand what practical security means for a real business.
NITECHSPARK is a formally registered Micro, Small and Medium Enterprise based in Erode, Tamil Nadu, India.
Assessments are led directly by the founder — not delegated to junior staff or outsourced teams. You work with the person doing the work.
Assessments follow a consistent, structured methodology across nine defined areas — not an informal checklist.
All assessments begin with a defined, written scope. We only assess what is agreed and authorized — nothing beyond that.
Findings and sensitive environment details are handled confidentially. NDAs are available subject to engagement terms.
Findings are documented in a professional report written for business owners — not just technical staff. Clear language, clear actions.
We don't just report problems. NITECHSPARK can implement the agreed corrective actions — we stay engaged through to resolution.
We tell you what we find — clearly and honestly. No inflated risk claims. No upselling of services you don't need.
NITECHSPARK helps MSMEs identify, understand and reduce practical cybersecurity and IT infrastructure risks. We are a focused technical company — not a generic IT outsourcer, not a product vendor. We do one thing well: structured assessment and practical remediation for businesses that depend on their IT environment.
We work with Tamil Nadu MSMEs and businesses across India that want honest, professional advice about their actual security posture — not sales pitches or compliance theatre.
Founder & CEO, NITECHSPARK
Nithyananthan brings hands-on technical experience across Linux server administration, infrastructure management, network security, and IT troubleshooting. NITECHSPARK's assessment methodology is built on real-world technical knowledge — not generic compliance checklists.
The assessments and remediation work are delivered personally — you work directly with the person reviewing your environment.
Everything you need to know about the NITECHSPARK assessment and remediation process.
An SME cybersecurity assessment is a structured review of your business's IT environment — including servers, endpoints, network, access controls, backups and websites — to identify security weaknesses, infrastructure gaps and operational risks. NITECHSPARK documents every finding, classifies risks by severity and business impact, and provides a practical roadmap showing what should be fixed and in what order.
Yes. The assessment scope and depth are adjusted to the size and complexity of your organisation. Whether you have 5 employees and a single server, or 100 employees with complex infrastructure across multiple locations, NITECHSPARK tailors the engagement to your actual environment. The Essential package is designed specifically for smaller businesses.
No. The assessment is not dependent on ISO 27001 or any other certification. It is designed for practical MSME environments, not compliance frameworks. We assess what actually exists in your infrastructure — not against a formal certification standard. If you are pursuing ISO 27001 or similar certifications, the findings can support that process, but it is not a requirement.
NITECHSPARK can assess servers (Linux and Windows), endpoints, network devices, firewalls, VPN configurations, websites, domains, DNS configurations, SSL certificates, cloud services and other authorized infrastructure within the agreed scope. The scope is defined and agreed in writing before the assessment begins — we only review what is explicitly authorized.
Yes. After the assessment, NITECHSPARK provides a separate remediation service to implement the agreed corrective actions. This is quoted separately based on the specific findings, their complexity and the implementation scope. We do not bundle remediation into the assessment — it is scoped and priced based on what your environment actually needs.
No. An assessment identifies risks within the agreed scope at the time of assessment. It does not guarantee complete security. Threats evolve, environments change, and no assessment can account for every possible risk or future attack. What it does is give you an honest picture of your current risk posture and a practical roadmap to reduce it.
Any intrusive testing or vulnerability scanning is performed only with explicit written authorisation and within the agreed scope. This is discussed and agreed during the scoping phase — before any work begins. We do not perform any active testing outside the agreed boundaries. Basic external exposure checks and port analysis may be included in the assessment scope where authorized.
Many assessment activities can be performed remotely with appropriate access and cooperation. Some elements may require on-site review depending on the environment and scope — particularly for network infrastructure and physical security considerations. Whether remote, on-site or a combination is appropriate is discussed during the discovery call and reflected in the agreed scope.
Tell us about your business and IT environment. We'll follow up with a brief discovery conversation to understand your situation and confirm the right assessment scope.